
What Really Happens When You Enter a URL?
Ever wonder what really happens when you type a domain into your browser? It kicks off a chain of protocols — and one of the most important is DNS.
what is DNS?
DNS is one of the basic services of the Internet. It is like a huge telephone book, which saves the mapping relationship between domain names and IP addresses.
When we type a URL into the browser, such aswww.123.com, the DNS service looks up and returns the IP address of the domain name, such as 192.0.0.1, and the device can then access the target site through this IP address.
With DNS, users don't have to remember complex numeric IP addresses, just easy-to-understand domain names to access websites.
DNS, important but fragile
Although DNS is crucial to the Internet, this basic service is fragile.
DNS is frequently targeted in cyber attacks. For example, 'DNS hijacking' is a common type of attack where attackers modify DNS records to redirect users to fake, malicious websites. This way, users might unknowingly enter their personal information or login credentials, falling into the attacker's trap.
In addition, DNS is also vulnerable to cache pollution, DDoS attacks and other threats. Once DNS fails or is attacked, it will directly affect users' Internet access.
The vulnerability of DNS forces us to seek additional security measures, andDNS proxyis one solution.
What is a DNS proxy and what does it do?
DNS proxy (DNS Proxy) is a "relay station" between the user's device and the DNS server. It receives the user's DNS query request, processes it, and then forwards the request to the appropriate DNS server.
When managing networks, we typically use methods like DHCP to uniformly assign DNS server configurations to user terminals. However, users often modify these settings arbitrarily or malicious software can interfere, leading to a variety of DNS servers being used by different terminals. This not only complicates management but also makes it easy for users' DNS requests to be redirected to malicious websites, ultimately posing a threat to users.
The DNS proxy can centrally manage the DNS resolution process. In the above case, when the DNS proxy forwards a user's DNS request, it can convert the destination address of the DNS request packet and forward the DNS request to a secure DNS server.
In other words, no matter what DNS server is set by the user terminal, the DNS proxy will eventually send the user's DNS request to a trusted DNS server, such as 114.114.114.114. This can effectively prevent DNS hijacking and protect users from malware.
On the other hand, DNS proxies can also enhance users 'network experience. In scenarios with multiple lines and operators, DNS proxies can intelligently manage and optimize the distribution of DNS requests based on different lines and operators. For example, when a user needs to access resources from Telecom, the DNS proxy will forward the request to Telecom's server, thereby reducing network latency and improving access speed.
In addition to the address translation of packets mentioned above, DNS proxy usually has DNS cache, DNS load balancing, DNS filtering, custom resolution and other functions, providing users with powerful network management, optimization and security control capabilities.
Panabit version update: WAN line DNS proxy
In the latest release of Panabit TANGr6p3, we introduce a new feature: WAN line DNS proxy.
Panabit's original DNS control function also has the ability of DNS proxy.
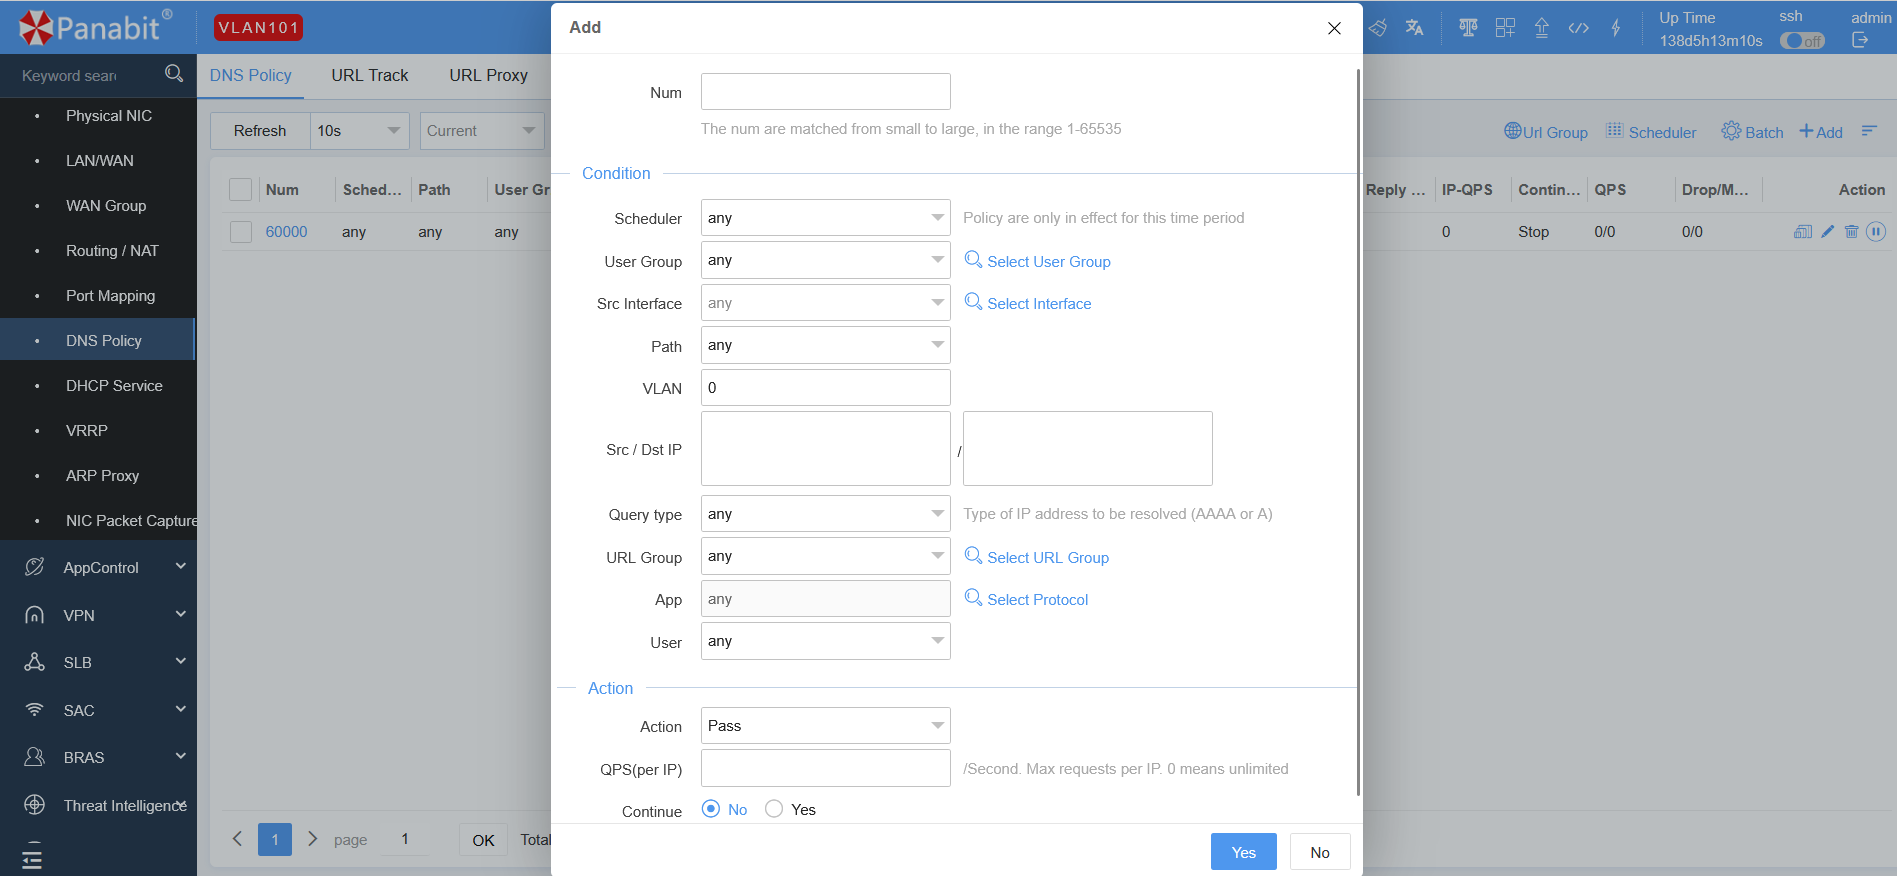
In this update, the "DNS proxy" option is added directly to the WAN line, making configuration easier.
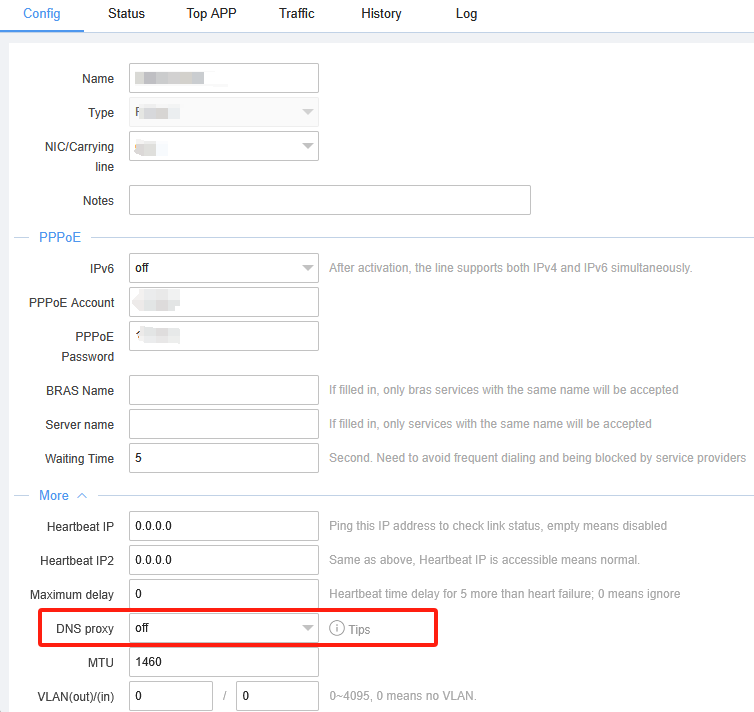
▶ Remind: The priority of DNS control is higher than that of line DNS proxy.
After the WAN line is enabled, all DNS requests that pass through the WAN line for NAT will automatically convert their destination address to the DNS address of the line to avoid DNS resolution problems.
In the enterprise/park network, through unified DNS resolution management, DNS proxy can effectively prevent DNS hijacking on the one hand; on the other hand, especially in the scenario of multi-operator export, combined with Panabit's application-level export load balancing, DNS proxy can also help users to optimize the network and improve the user's network experience.
▶Other updates
In addition to the DNS proxy, the Panabit TANGr6p3 has the following updates:
▎ New features
● IPv6 is supported in GTP decoding
GTP (GPRS Tunneling Protocol) is a set of IP-based high-level protocols, mainly used for traffic transmission between operators' mobile core networks.
The new version adds the ability to parse IPv6 in GTP packets and identify IPv6 traffic transmitted through GTP tunnels.
▎ Function optimization
● DHCP Server module
1. Improve the processing mechanism of relay messages by DHCP Server to ensure that DHCP response messages can be correctly returned to the DHCP relay service that initiated the request.
2. Improve the DHCP address allocation algorithm. DHCP Server can select the matching DHCP server and address pool according to the IP address of DHCP relay service, so as to make the IP address allocation more accurate and enhance the support for relay services in different network segments.
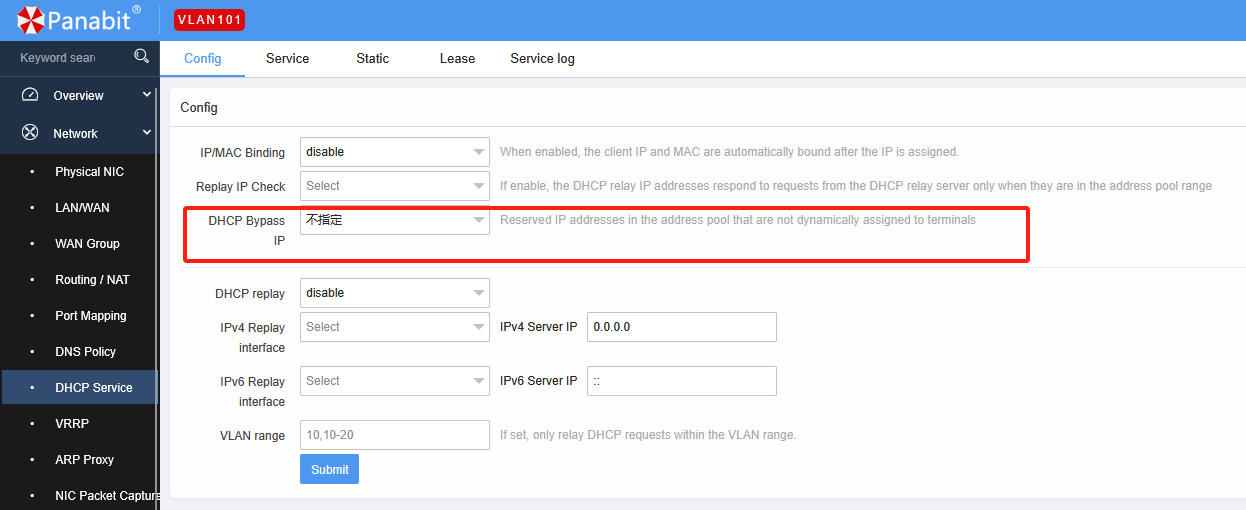
3. Add an exclusion IP group, in which the IP addresses will not be dynamically assigned to terminals by DHCP Server.
4. For wireless APs that support master/backup policies (such as Panabit AP, which can communicate with Panabit's SAC and SaaS cloud platform at the same time), we have improved DHCP Server to enable it to issue addresses for two wireless controllers simultaneously.
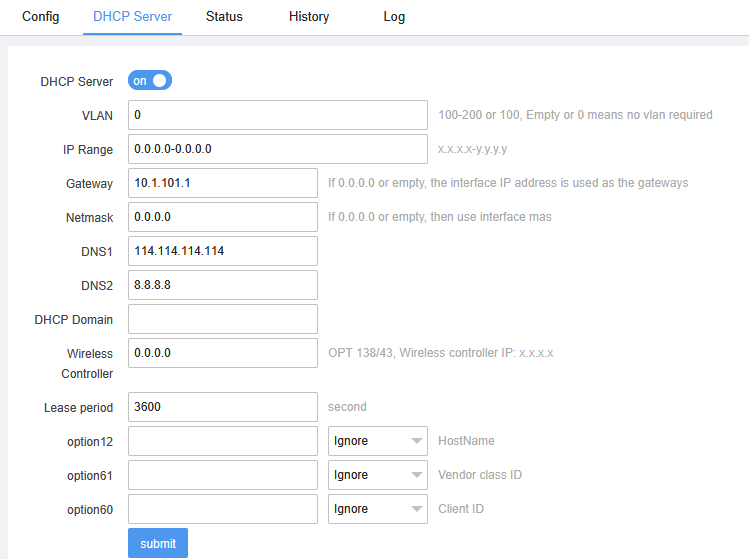
5. Add IP/MAC binding error packet loss counter to record packet loss events caused by IP and MAC mismatch, so that network administrators can monitor and analyze security events.
● Port mapping module
1. Remove the restriction that the policy ID cannot be greater than 65535 (port mapping policy entries are unlimited).
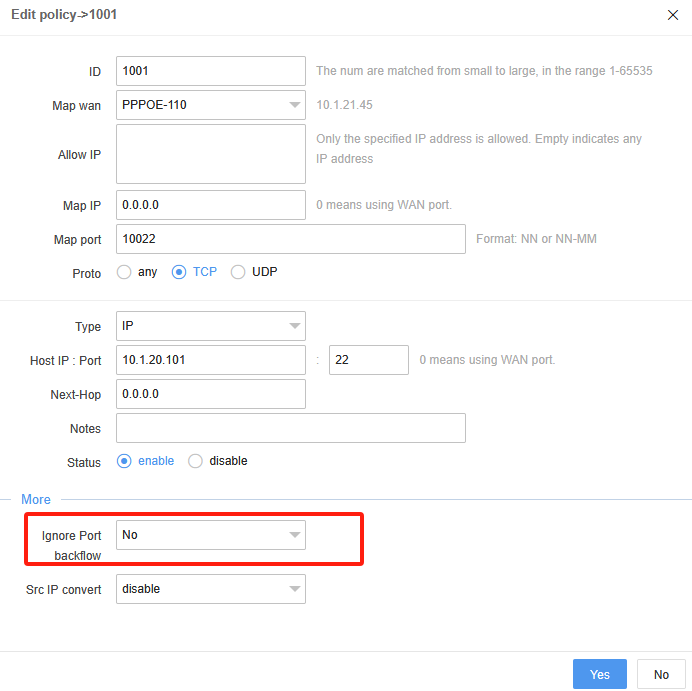
2. The port mapping policy adds the option of not returning, and the policy configuration is more flexible.
● Network traffic output display
If the list command is added to floweye, and shownum is set to 1, the rate is displayed as an actual number without unit conversion.
● SLAAC stateless address allocation
Optimize the SLAAC stateless allocation process to ensure that the client can correctly obtain DNS configuration while obtaining IPv6 address.
● Drive optimization
1. Add support for giant frames. The MTU value of the network interface can be modified through the /etc/PG.conf configuration file.
2. Add network card power management support to the network. You can use the command to control the power on and power off of the network card: floweye if set name=network card name power=off|on.
● Connection number control
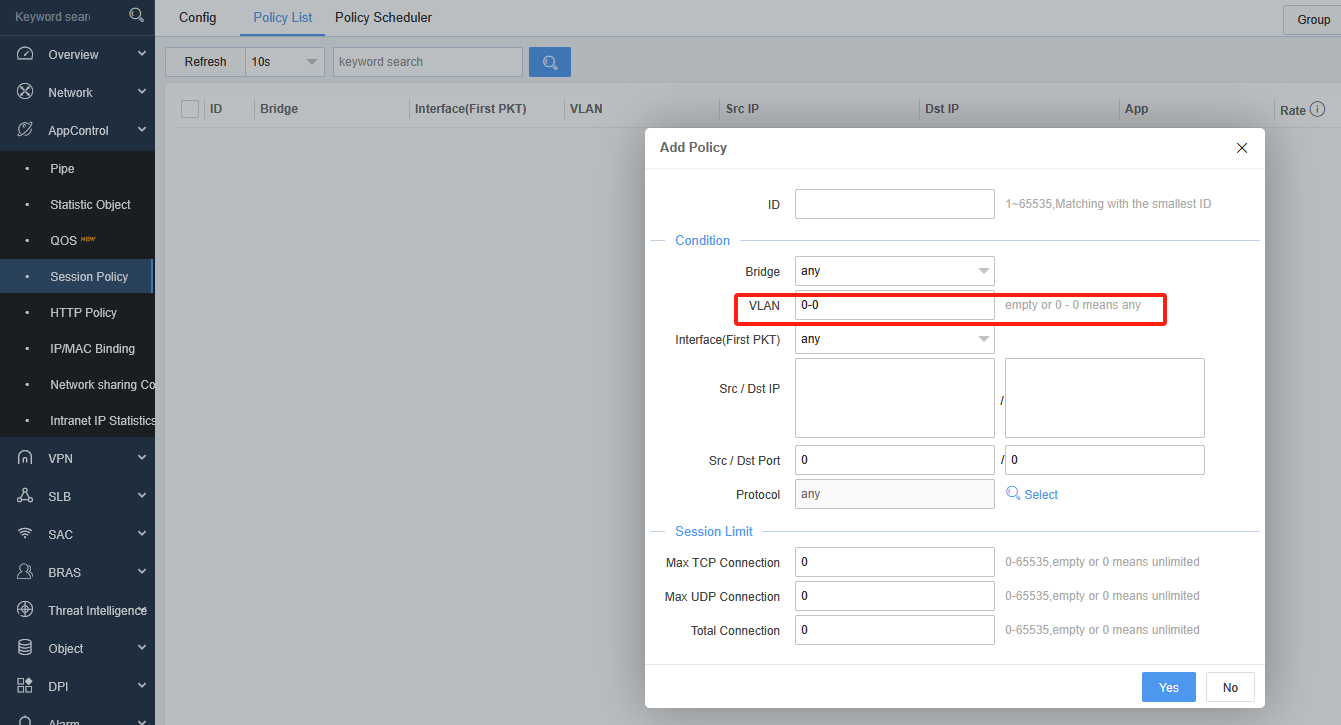
Add VLAN conditions to the connection control policy.
● TCP connection aging mechanism
The TCP connection aging mechanism is improved. For a half-connection TCP session with only three handshakes but no data, the system does not delete it by default.
● Flow control policy
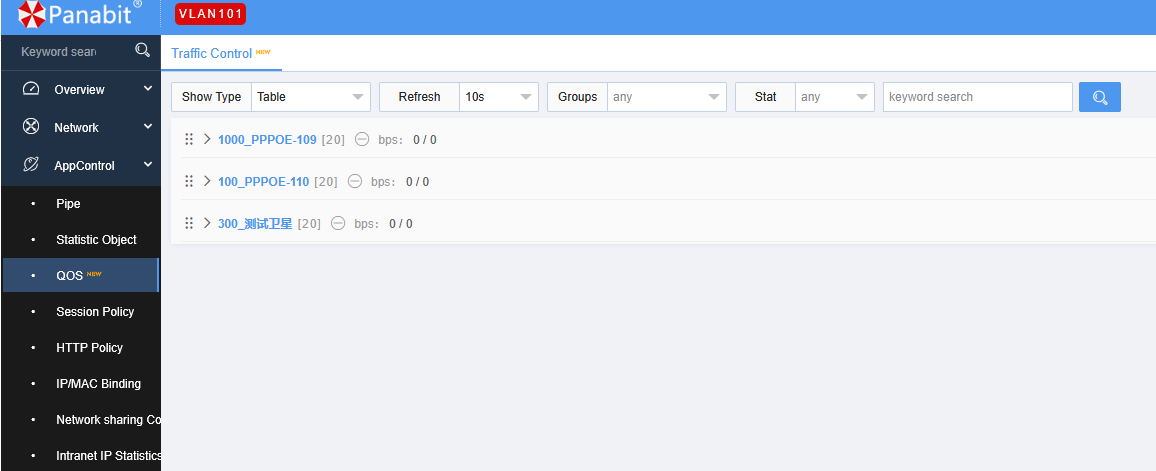
Increase the maximum number of concurrent strategies to 16,000.
Attention:
There are too many policies in a single policy group. When the policy group is expanded, the page loading time will be longer.
▎ Page optimization
● Traffic control policy
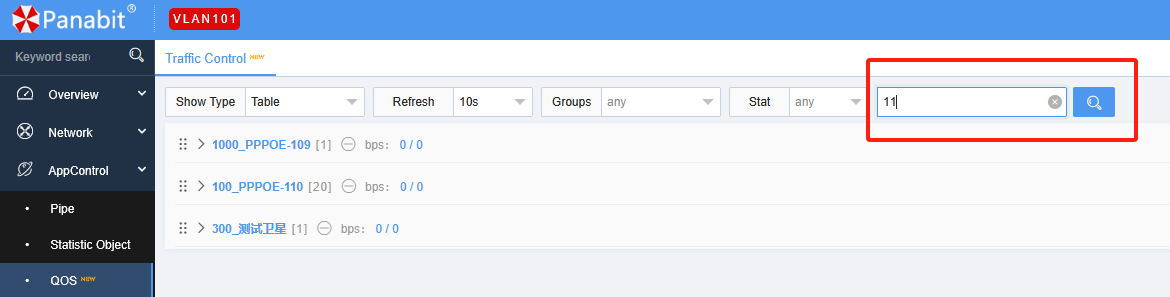
1. Optimize the keyword search of new flow control, which can be achieved through specific keyword search strategies. (IP group keywords and Chinese keywords are not supported)
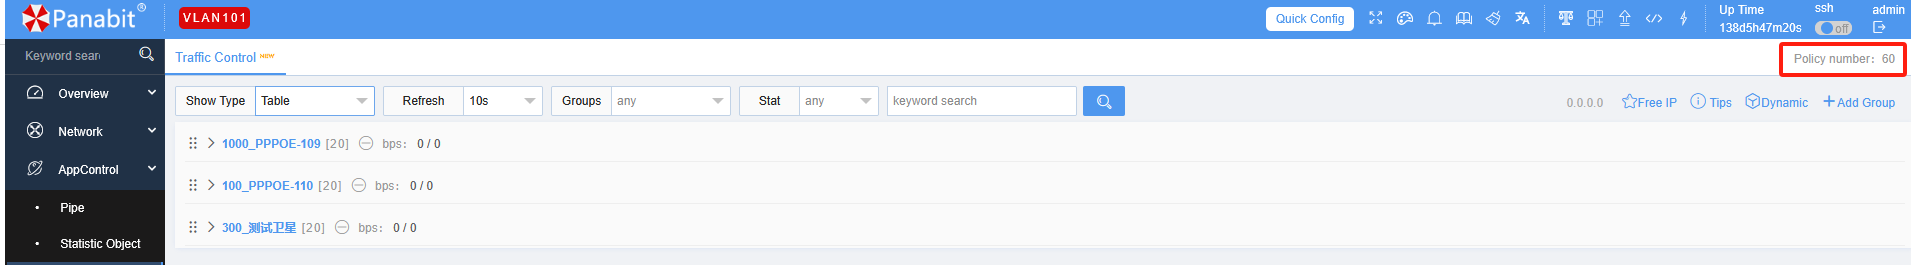
2. Increase the number of statistics for all strategy entries
● AP import function
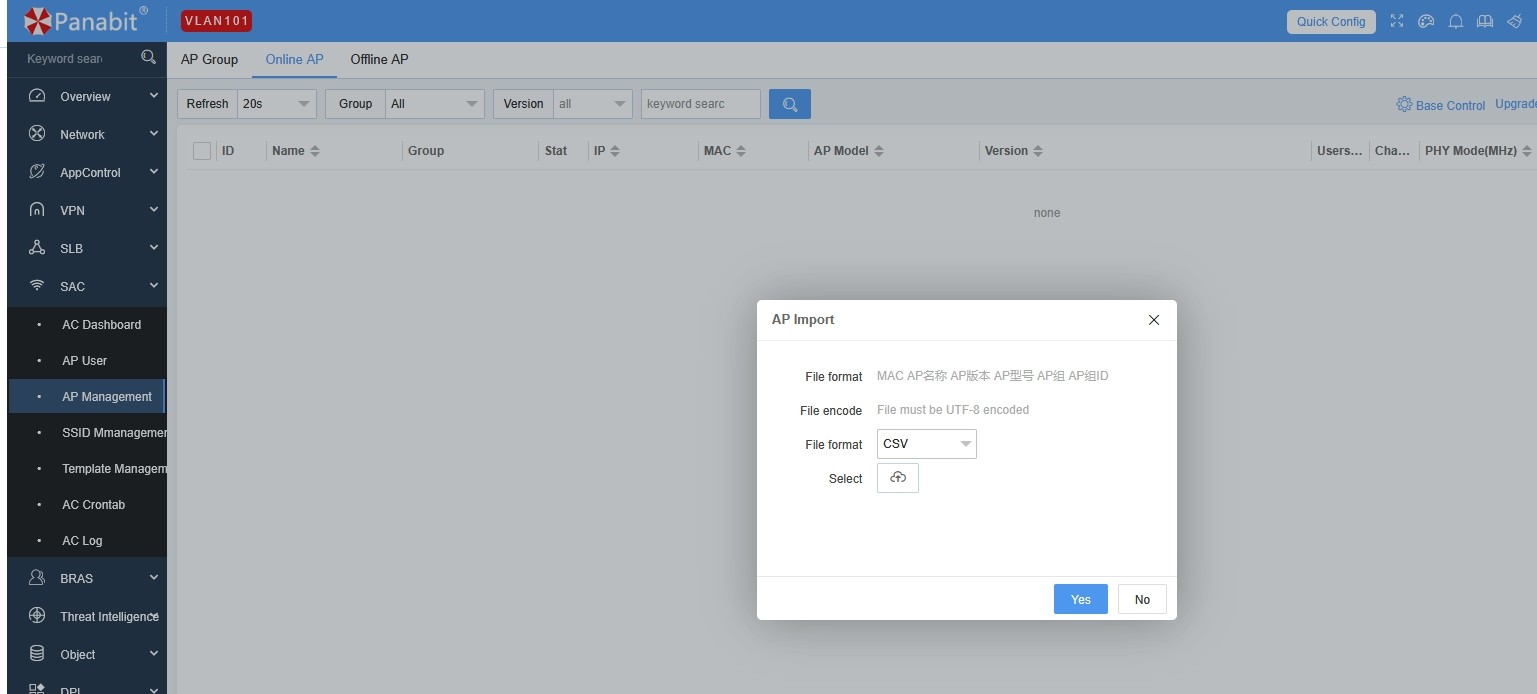
Support for CSV import format is added to AP management
● organizational structure
The organizational structure adds a scroll bar to avoid sharing the scroll with the account page, making it easier to configure and view.
● Other optimizations
1. Custom protocol group configuration page: Optimize the page for editing members of custom protocol groups, and do not display custom protocol groups to avoid configuration errors.
2. Ping monitoring: Expand the number of Ping measurement objects, add up to 512 items, record alarm logs and save 2000 items.
3. Ping function page: The management port ICMP Ping and TCP Ping can work simultaneously.
▎ Feature library update
● 29 new protocols such as DailyMetion
● Updated 24 protocols such as "NetEase CC"